Know what the underground knows about you.
Dark web markets, ransomware leak sites and vulnerability chatter, monitored where most vendors have no visibility and investigated before it reaches your perimeter.
What this covers
Most intelligence products tell you what is happening in the world. Overwatch tells you what is happening to you, then works the case. Collection runs continuously across underground forums, marketplaces, leak sites and messaging channels, including the non-English communities where much of the activity targeting enterprises begins. Agents verify what they find, map it to your assets, vendors and business units, and hand your team a finding with the evidence attached.
Capabilities
- Dark and deep web monitoring
- Ransomware leak site tracking
- Third-party and vendor compromise
- IOC, TTP and CVE intelligence
- Compromised credential monitoring
- Non-English underground coverage
Detect
Continuous collection across forums, markets, leak sites and channels, with classifiers turning billions of events into candidate signal.
Investigate
Agents verify exploits, map actor infrastructure, pair credentials against breach corpora and assemble the evidence package.
How investigations workAct
Validated findings routed into SIEM, SOAR or case management, with analyst briefings on the cases that need a human answer.
Sample output
A finding, with the evidence attached.
- Customer
- Kestrelmoor Bank
- Vendor
- Fernhollow Payroll
- Vendor domain
- fernhollow-payroll.example
- Claimed data
- 410 GB, HR and payroll records
- Group
- Tracked as RG-112
- Posted
- 2 days ago
Exposure assessment
- Fernhollow Payroll holds employee payroll data for three Kestrelmoor Bank business units
- The Fernhollow portal is connected to Kestrelmoor single sign-on
Affected assets
- Employee records, three business units
- Vendor portal SSO integration
Recommended action
Confirm scope with Fernhollow, review the SSO connection and brief HR and legal before the group publishes a sample.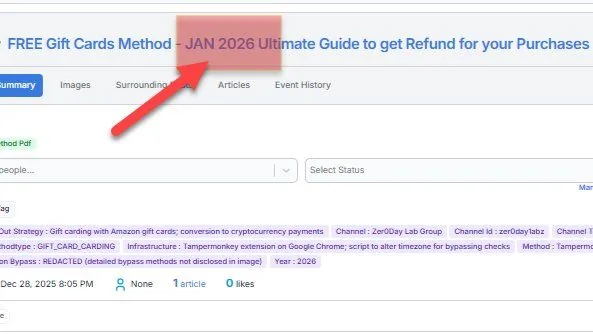
Questions
How is this different from a threat feed?
A feed gives you indicators. Overwatch gives you the investigation that turns an indicator into a decision, with the sources it consulted recorded.
Does it cover non-English sources?
Yes. Collection reaches the non-English underground communities where much of the activity targeting enterprises begins.
Stop chasing alerts. Start working ahead of them.
Overwatch turns real-time understanding of the criminal underground into the investigations and risk decisions your fraud and security teams have to make every day.