See the method before it reaches your customers.
Compromised data and the techniques being weaponized against your organization, from account takeover and card fraud to fraud rings and insider threats.
Detections
Detected in monitored channels
Investigation
Untitled · 10-06 09:41Kestrelmoor card batch
One seller, Tallowmark, is moving a batch of 14 full card numbers from a single Kestrelmoor BIN. The listing went up on a carding marketplace and is being promoted on Telegram.
Tallowmark posts the same batch in # Tallowmark Shop8 msgs, # Greywick Exchange5 msgs and # Wrenhollow Chat3 msgs, and points buyers to a private channel.
Sellers and channels discussing KestrelmoorSource ↗
Tallowmark posts the batch into 3 channelsConfidence
- High — The listing is live: 14 cards from one Kestrelmoor BIN, with samples posted.
- High — One seller, Tallowmark, is behind the listing and the Telegram posts.
- Medium — Same card base as an earlier Tallowmark batch.
- Low — The seller's claimed balances and valid rate.
Investigations
Manage and track your security investigations
9 investigations found
Kestrelmoor BIN card batch
Fourteen full card numbers from one Kestrelmoor BIN on a carding marketplace. The seller also posts in three Telegram channels; six messages attached as evidence.
View DetailsNew-device check bypass
A Telegram post sells a method for getting past Kestrelmoor’s new-device checks. Agents are matching it against recent account takeover reports.
View DetailsStaff logins in a stealer log
Three corporate logins for Kestrelmoor staff found in an infostealer log. Each one was matched to a current employee account and sent to the security team.
View DetailsBranch staff recruitment
A Telegram post offers payment to bank branch staff for customer lookups. Agents are tracking the poster across other channels.
View DetailsLookalike login domain
kestrelmoor-verify.example served a copy of the online banking login page. The evidence package went to the brand team for takedown.
View DetailsPayroll vendor data leak
A ransomware group posted data it says came from a payroll vendor Kestrelmoor uses. Agents are checking the sample for employee records.
View DetailsExecutive exposure review
Exposure review for five Kestrelmoor executives: home addresses on data broker sites, two impersonation accounts and public travel mentions.
View DetailsBanking logins in a combo list
Thirty-eight Kestrelmoor online banking logins posted to a paste site. Most pairs match an older breach; six are new.
View DetailsAccount mule recruitment
Social posts offer cash to Kestrelmoor customers who rent out their accounts. Four posts trace back to the same recruiter.
View DetailsCard: 52•• •••• •••• 4417
Card: 52•• •••• •••• 8062
Card: 52•• •••• •••• 1295
Card: 52•• •••• •••• 4417
| Type | DEBIT |
| Bin | 52•••• |
| Last 4 | 4417 |
| Expiration | 08/2029 |
| Number | 52•• •••• •••• 4417 |
| CVV | ••• |
| Compromise Date | 2026-09-30 |
| Found In | Tallowmark Shop |
| Filename | fresh_14pcs[.]txt |
| Source | Telegram |
Comments:
Blocked and reissued all 14 cards. Watching the seller for new batches.
What this covers
Fraud teams are not short of alerts. They are short of the context that turns an alert into a decision. Overwatch collects the tools, methods and stolen data circulating in fraud channels, works out which of it points at you, and returns findings your team can act on: which BINs are listed, which combolists contain your customers, which method is being shared this week and exactly how it works.
Capabilities
- Account takeover
- Card and payment fraud
- Fraud rings and marketplaces
- Tools and methods
- Insider threats
- Compromised data monitoring
Detect
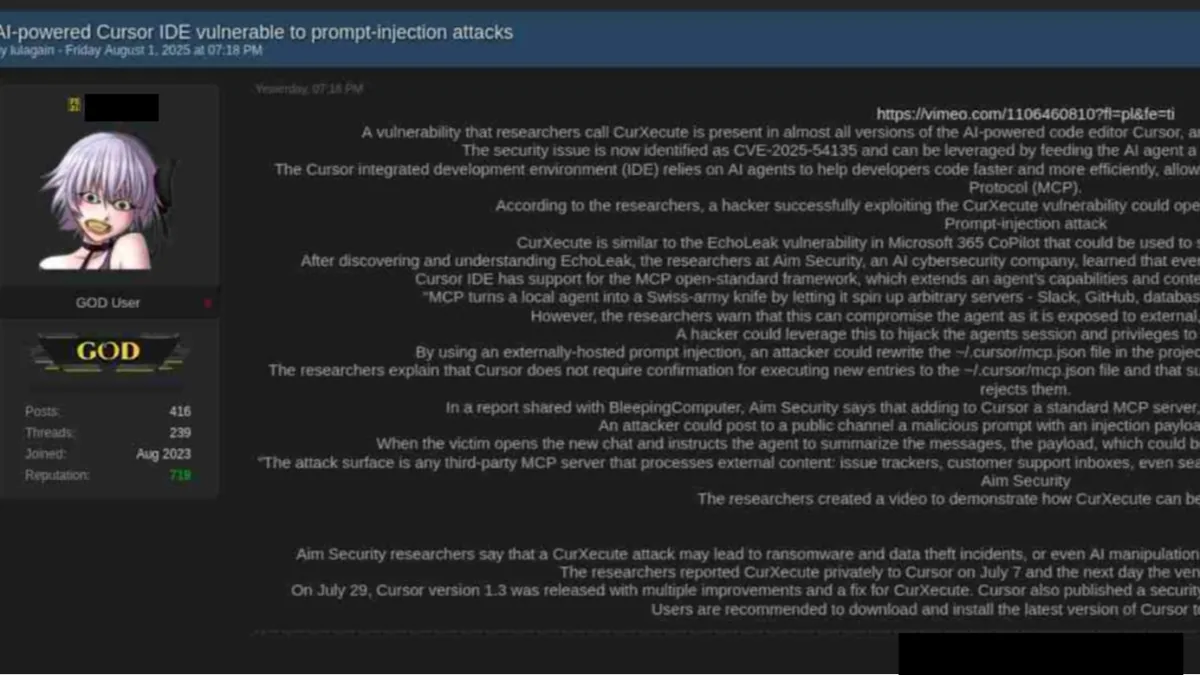
Continuous collection across fraud channels, marketplaces and messaging platforms, including image-based material such as receipts, balance screenshots and phishing kits.
Investigate
Agents verify listings against issuer records, map seller aliases across channels and pair compromised data with your customer base.
How investigations workAct
Findings routed to fraud operations with the evidence attached, including card reissue lists and prioritized actions.
Sample output
A finding, with the evidence attached.
- Customer
- Kestrelmoor Bank
- Channel
- Fraud channel, invite-based
- Lines in list
- 18,240
- Matched to Kestrelmoor customers
- 1,312 accounts
- Logged in last 30 days
- 214 accounts
- First seen
- 6 hours ago
Population affected
- 1,312 customer accounts with exposed credentials
- 214 of them active in the last 30 days
Recommended action
Force password resets on the matched accounts and step up authentication on the 214 active ones.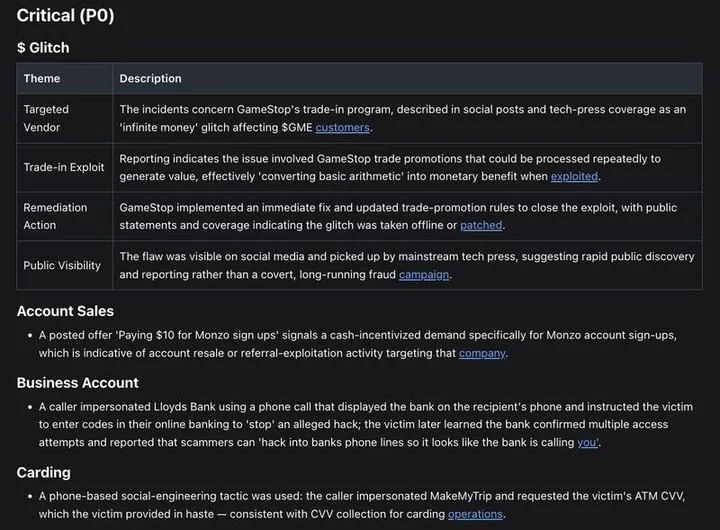
Questions
Can you tell us whether our customers are in a given breach?
Yes. Agents pair compromised data against your customer base and return the population affected, not just the existence of the leak.
What happens to the hard cases?
They escalate to Overwatch analysts, who validate the finding and write the briefing. Customers can reach them directly.
Stop chasing alerts. Start working ahead of them.
Overwatch turns real-time understanding of the criminal underground into the investigations and risk decisions your fraud and security teams have to make every day.